Reviewed and updated: 23 October 2026.
A cloud-security review should help your team answer three questions: what needs attention, who owns the next action, and how will you confirm it was resolved? A long findings list alone does not answer them.
For Malaysian organisations using Google Cloud and Google Workspace, the starting point also matters. GCP infrastructure, Workspace accounts and shared files need different checks. This guide explains five mistakes to look for and how to choose a useful next step with MatrixC.
Review the five mistakes · Choose an assessment or product · Discuss your next review
Five cloud-security mistakes to check
1. Leaving responsibility between the provider and your team unclear
Moving a workload to Google Cloud does not remove your organisation’s responsibility for its access, configuration and data. Google describes cloud security as a shared responsibility. Its Well-Architected security guidance is a useful reference when deciding what your team must own.
Start with one important workload. Name its business owner and technical owner, identify the data involved, and record who approves access and changes. For Workspace, include the administrator responsible for accounts and external sharing. When responsibility sits with several suppliers, agree who follows up on a finding before the review starts.
2. Reviewing permissions without checking how people actually work
A broad administrator role, an old service account or a file shared outside the organisation may deserve attention. The next decision depends on why that access exists and what would stop working if it changed.
Ask the owner to explain the business need, then review whether the access is still appropriate. In Workspace, review third-party app access as well as user accounts. Google’s app-access controls help administrators review which applications can access Workspace data. Have the authorised administrator plan and approve changes; avoid revoking access blindly during a review.
3. Collecting alerts without assigning a next action
Google Security Command Center provides native risk-management capabilities, with coverage depending on tier and configuration. Review what is already enabled before deciding whether another product is needed.
For each finding your team accepts as relevant, record the affected service, business impact, owner and target review date. Distinguish a suspected active incident from a configuration improvement. A monthly report is useful only when someone reviews it and can explain what changed since the last one.
4. Treating a scan or compliance score as proof that everything is secure
A scan reflects its coverage, available evidence and the time it ran. A benchmark score cannot establish that every account, application and process is secure, or certify your organisation’s compliance.
Keep the scope beside the results: which projects or domains were included, which evidence was unavailable, and what needs a separate investigation. Ask for an explanation of important findings before using the report in a management or audit discussion. A read-only review can identify issues; it does not make the recommended changes for you.
5. Closing the report before checking the fix
Assigning an action is only the start. The service owner should approve the change, consider dependencies and rollback, and confirm the result afterward. An unused resource should not be deleted solely because it looks unnecessary in a report.
Use a short follow-up record: finding, agreed action, owner, completion evidence and next review date. Where risk is accepted rather than fixed, record who accepted it and why. This gives the next reviewer context and helps existing customers continue from the last review.
Which MatrixC security option fits your need?
GCP AuditGlance: infrastructure visibility
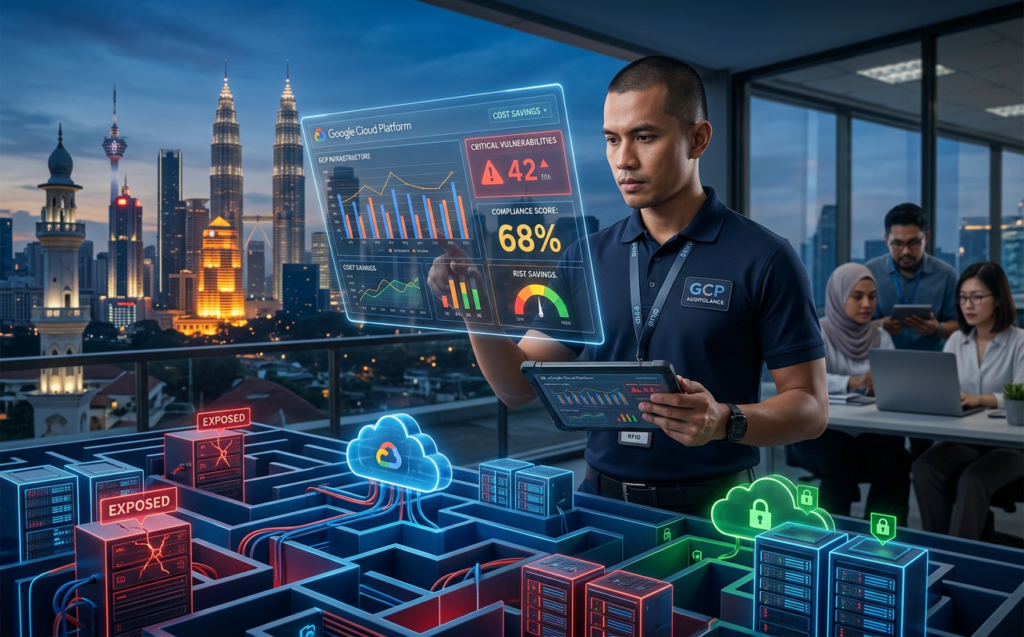
For teams reviewing Google Cloud projects, GCP AuditGlance brings asset visibility, security findings, recommendations and cost visibility together. A free entry tier is available. Check current plan limits before assuming scheduled reports or AI-assisted analysis are included.
Use the product’s current onboarding instructions with an authorised administrator. A findings dashboard does not authorise remediation or a billing transfer. Ask MatrixC separately about support or implementation scope.
GWS AuditGlance: recurring Workspace visibility
AuditGlance for Google Workspace supports recurring reviews of activity, user risk, sharing and security evidence. It is a separate product from the GCP scanner. Discuss coverage, edition dependencies, access and commercial terms with the team through the Workspace product enquiry.
MatrixC Workspace Security Assessment: a scoped review
For a human-led starting point, discuss a read-only, point-in-time review of agreed Workspace security evidence. Depending on scope and available evidence, this may cover identity and access, sharing, third-party apps and administrative controls.
Confirm the findings report, prioritised recommendations and findings review in your proposal. Configuration changes, ongoing monitoring, AuditGlance subscriptions, certification, penetration testing and incident response are separate from this assessment. Scope, evidence handling, fees and availability must be agreed before work starts.
Start with the question you need answered
Tell us whether your concern is GCP infrastructure or Workspace accounts and collaboration. Add the decision you need to make and your preferred timing. Existing customers can ask to review outstanding findings or changes since the last assessment.
WhatsApp opens with an editable enquiry draft. Prefer a website form? Contact MatrixC.
Please do not send passwords, tokens, service-account keys or confidential security exports through WhatsApp. The first conversation is to check fit. If you suspect an active compromise, contact your authorised security lead or incident-response provider; this assessment is not an emergency-response service.